
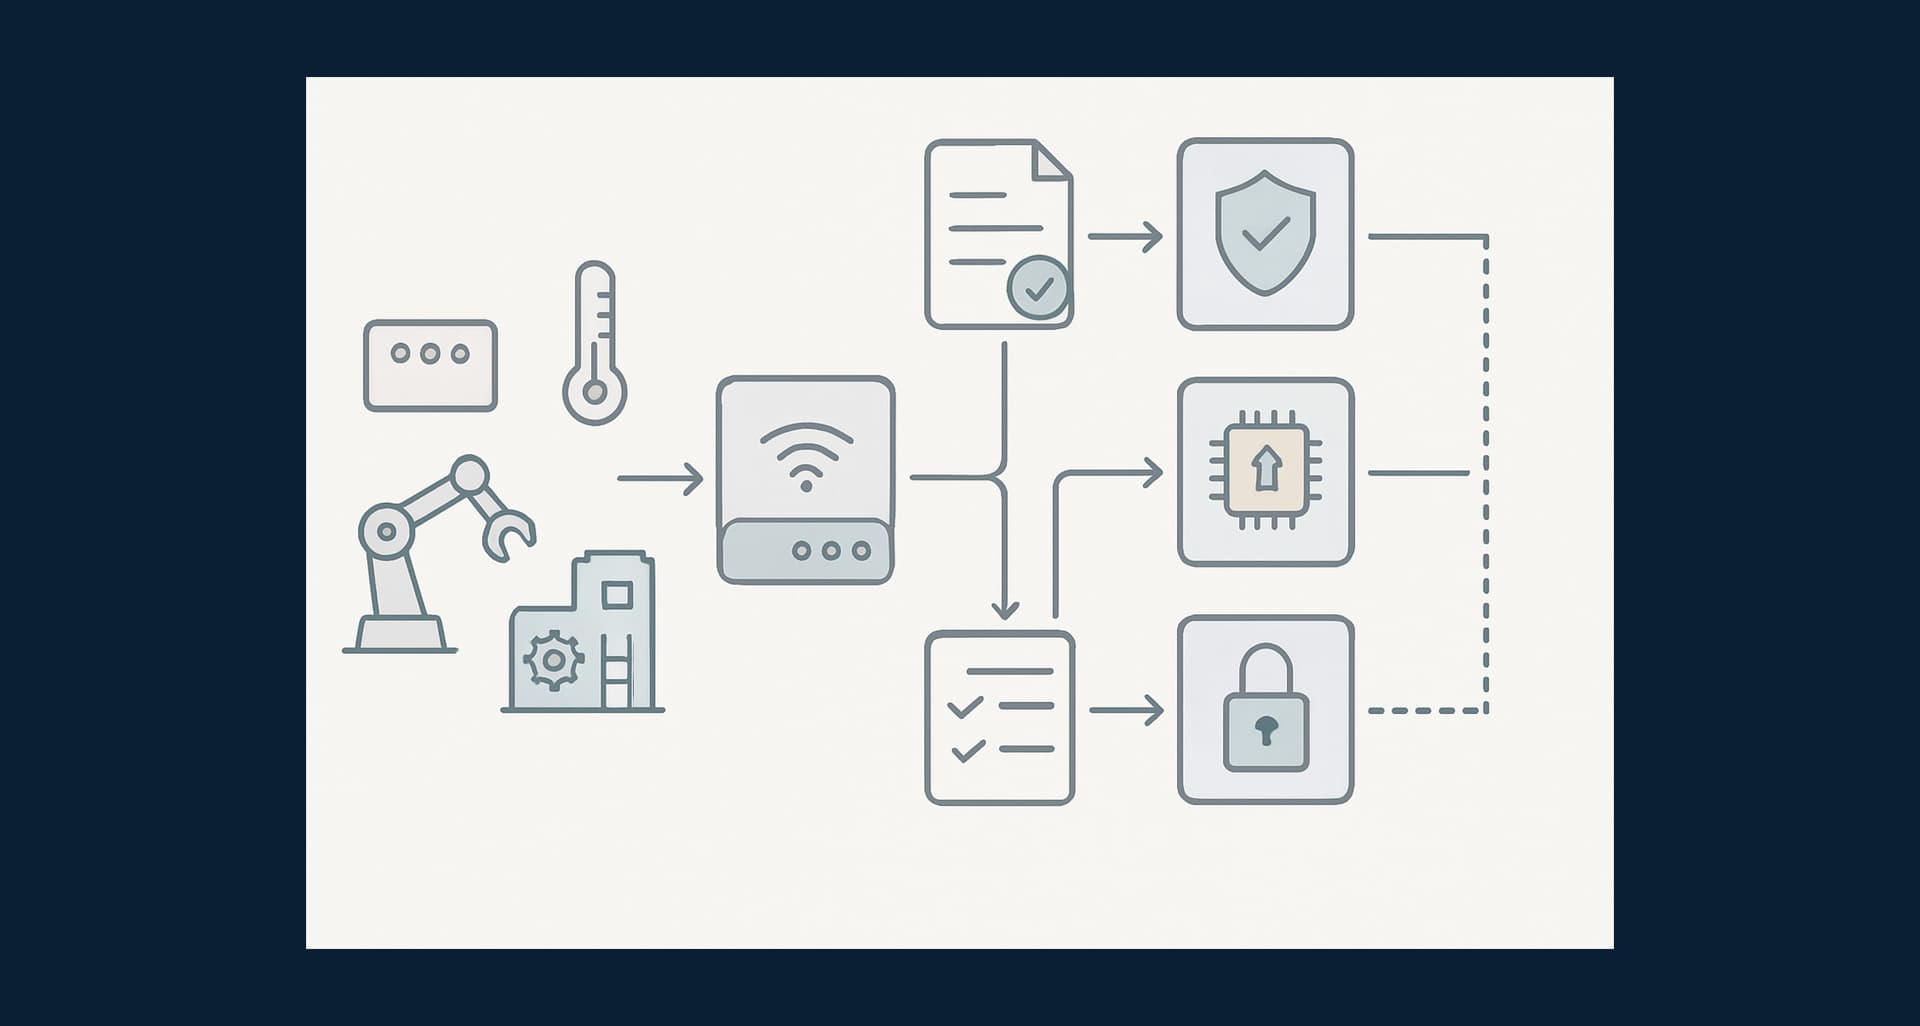
Device identity is a core requirement for secure edge infrastructure. Before an edge platform can trust data, accept commands, or permit access, it needs a way to verify the device on the other end. MeteorEdge is designed to support device identity through verifiable credentials, enrollment controls, and policy-aware communication. This helps teams confirm that known devices are the ones participating in edge workflows. A defined device identity model also improves visibility. Sensors, controllers, and gateways can be tracked as distinct assets rather than anonymous connections moving across the environment. With identity established at the start, security policies, telemetry handling, and lifecycle management have a more reliable foundation. That makes edge operations easier to structure and easier to audit.